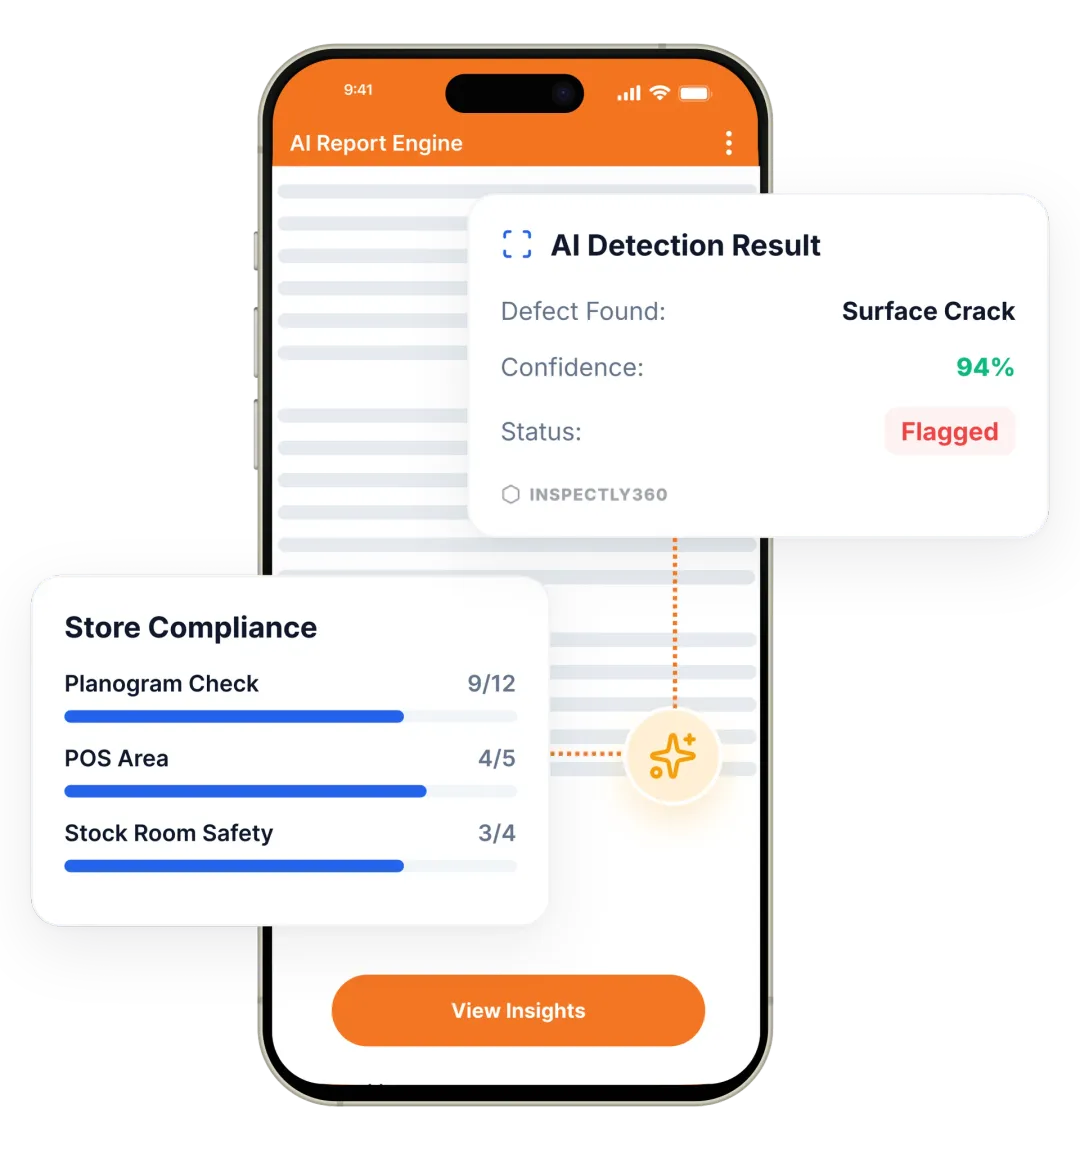
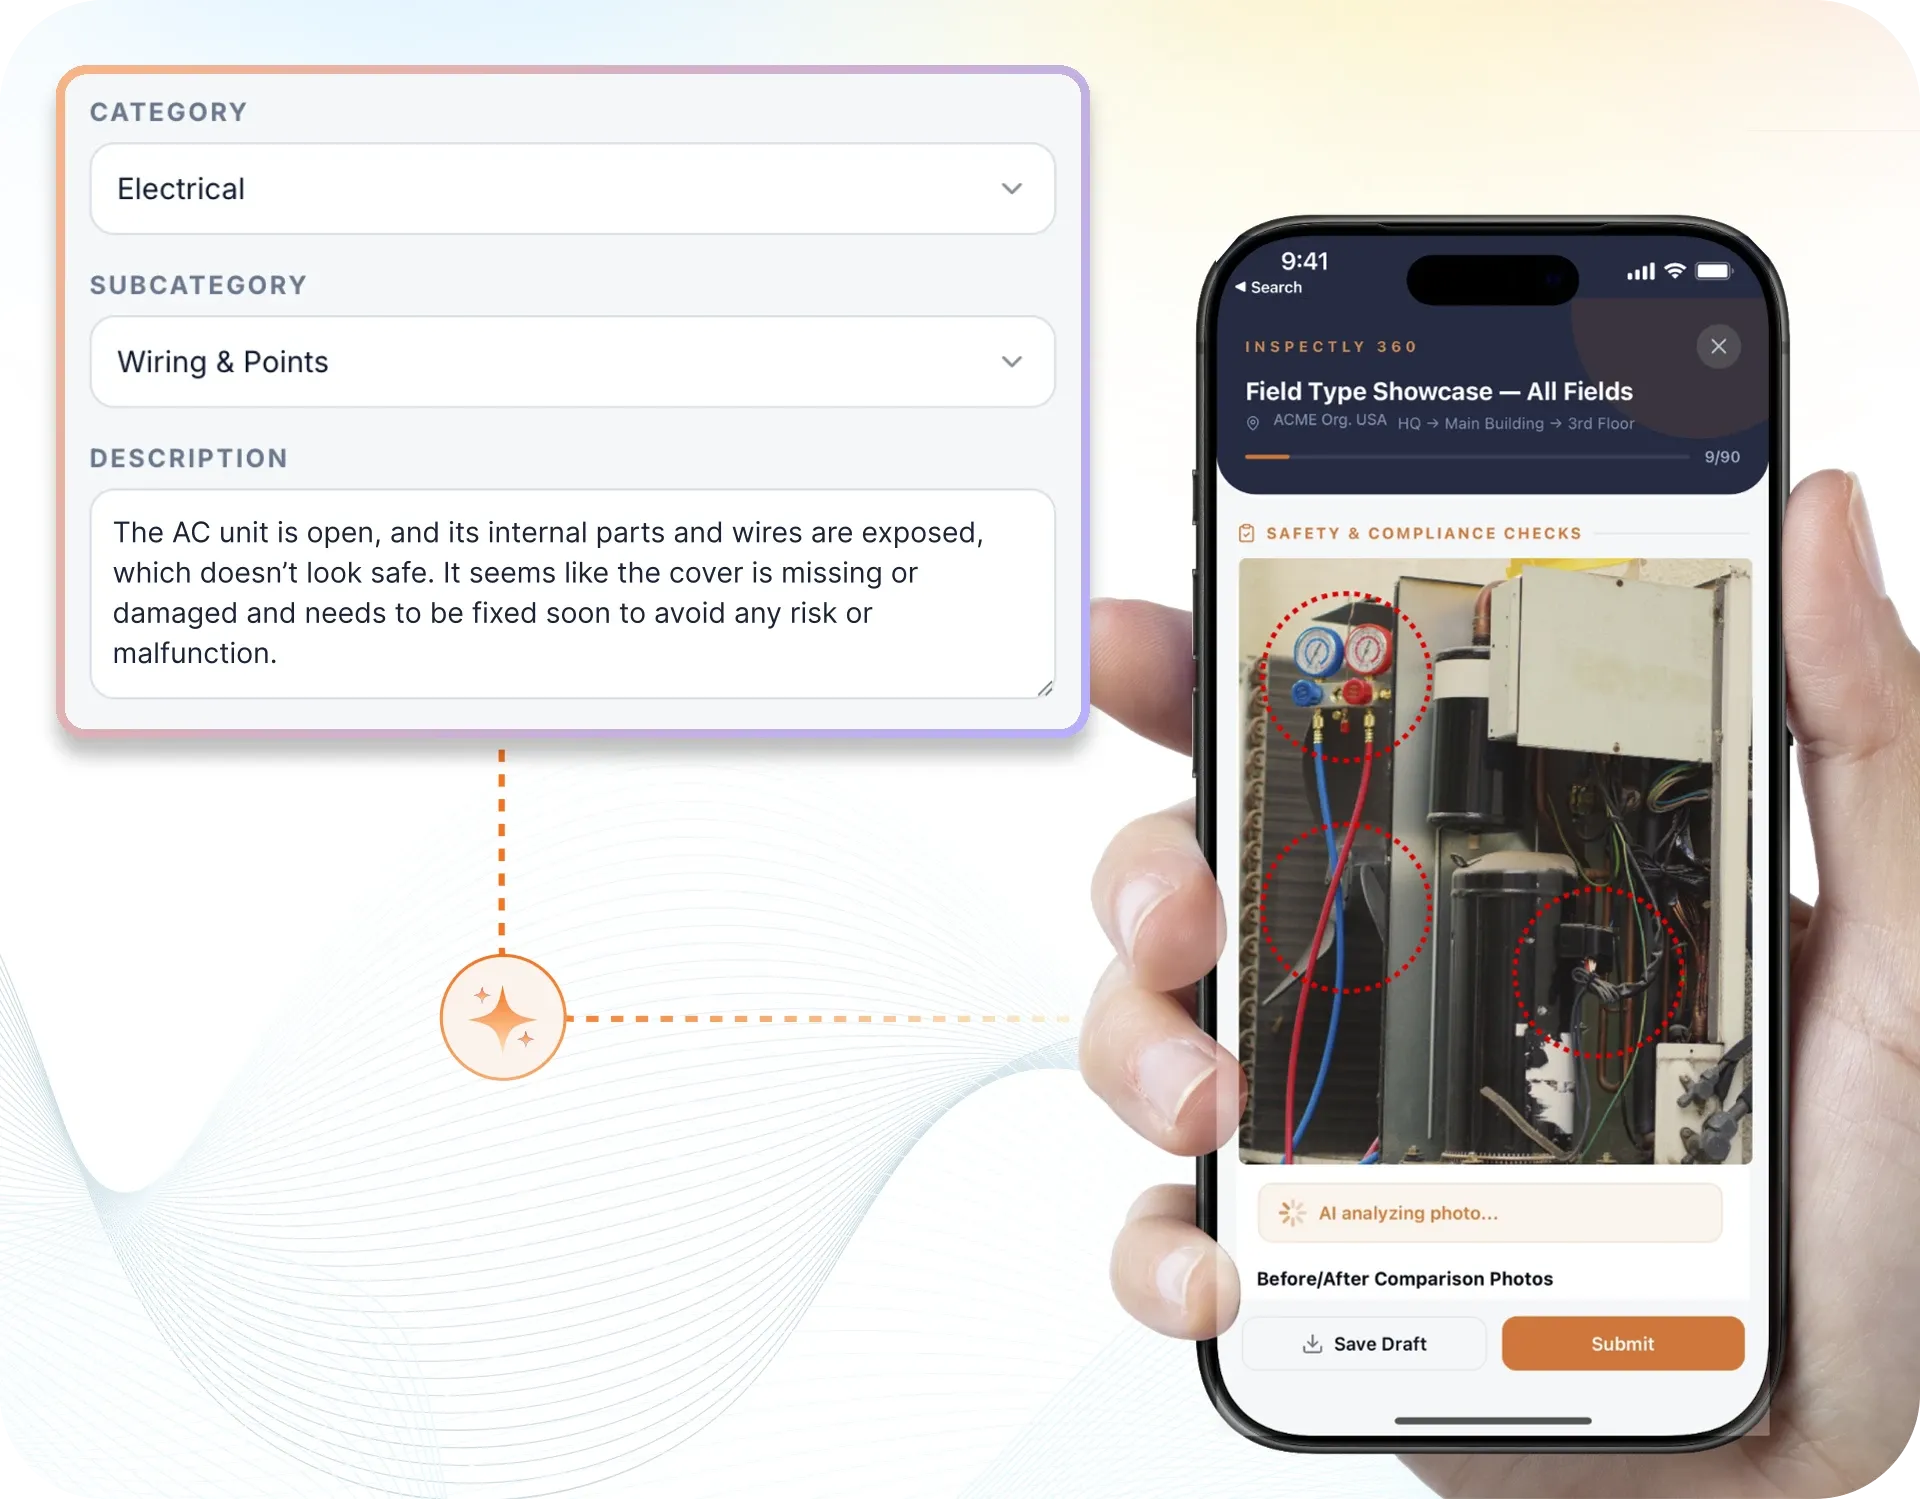
Take a Photo. AI Fills the Form
Your inspector takes a photo of any asset or defect. AI reads it and fills the inspection form automatically. No typing. No manual entry.
ISPS Security Audit App turns ISPS security audits into a scored, repeatable programme. Auditors score each asset against weighted criteria, attach photo evidence, and track corrective actions to verified closure across every site. Managers compare ISPS security audit scores across sites and track every corrective action to closure.
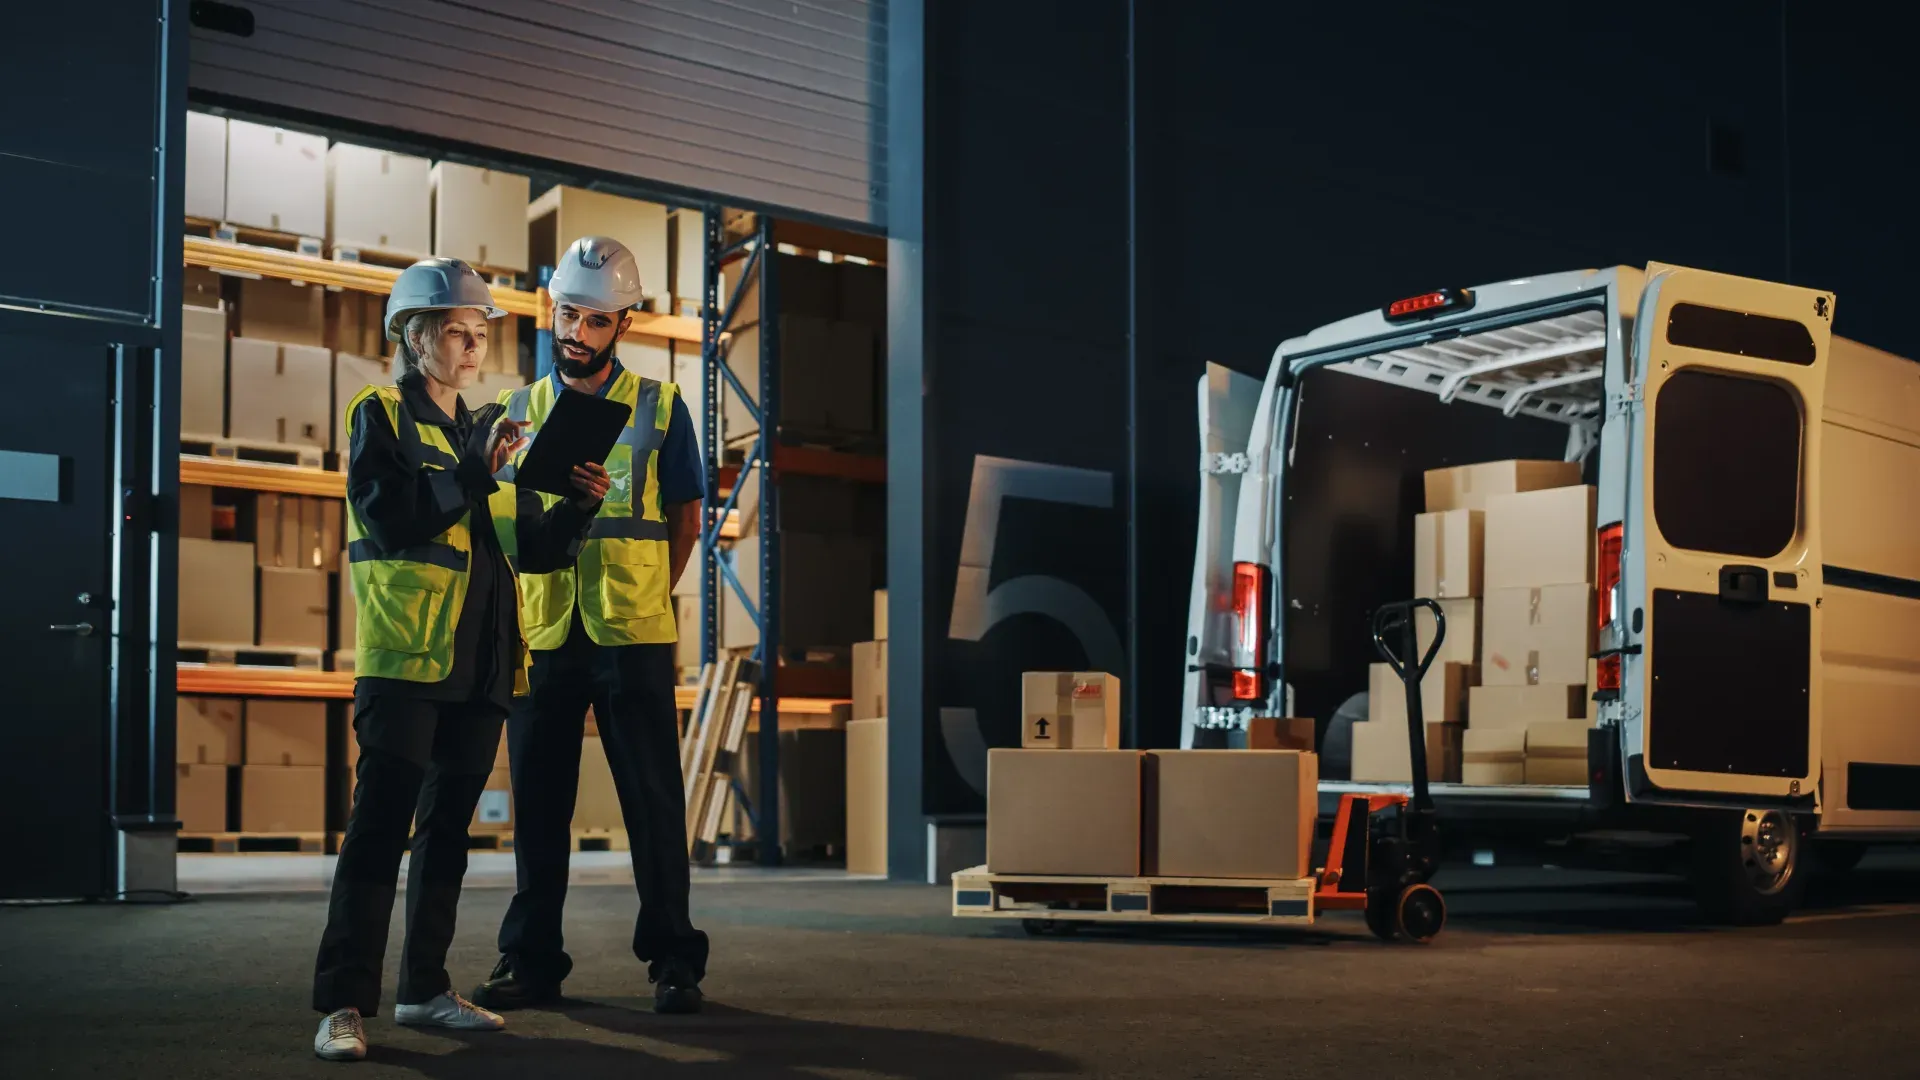
ISPS Security Audit App runs a scored ISPS security audit covering security level and declaration of security, access control and restricted areas, CCTV, lighting, and perimeter, security equipment and communications, and drills, records, and training, with a photo and a sign-off required on each point. Without a system, ISPS security findings live on paper and in chat. An ISPS security fault such as access control gaps at the security level slips through. An audit then means rebuilding ISPS security evidence from folders.
ISPS Security Audit App keeps one record per ISPS security and per site, with photo evidence and a named sign-off. Each ISPS security finding is tracked to verified closure. Ship and port facility security officers see ISPS security completion and overdue actions across the transport, logistics & warehousing portfolio. Every ISPS security record proves what was checked, when, and by whom.
A comprehensive ISPS security audit covers the key areas that affect telecom and data centre uptime, safety, and compliance. Audit ISPS security with structured access-control, surveillance, and SSP checks plus corrective action tracking. Your audit should include sections for security level and declaration of security; access control and restricted areas; and CCTV, lighting, and perimeter, evidence capture, pass/fail or scoring criteria, corrective action assignment, and sign-off, so that nothing is missed and every audit finding is traceable.
A scored audit only helps if every auditor scores the same way. Follow these steps to run an ISPS security audit:
An ISPS security audit scores condition against ISPS Code and SOLAS Chapter XI-2, checking security level and declaration of security, access control and restricted areas, CCTV, lighting, and perimeter, security equipment and communications, drills, records, and training, and ship security plan and alert system. Each ISPS security finding is logged with a photo, a severity, and the failing point. So the ISPS security audit becomes a traceable evidence pack, not an ageing spreadsheet.
Templates align to ISPS Code, SOLAS Chapter XI-2.

Weighted criteria are built into the ISPS security audit template.

Auditors attach photo proof for each ISPS security non-conformance.

Scorecards rank sites and failed ISPS security criteria become corrective actions.
Everything your field team records during ISPS security audit, from photos and voice notes to sign-off, InspectWrk turns into a finished report automatically. Faster, more accurate, and without the retyping.
Your inspector takes a photo of any asset or defect. AI reads it and fills the inspection form automatically. No typing. No manual entry.
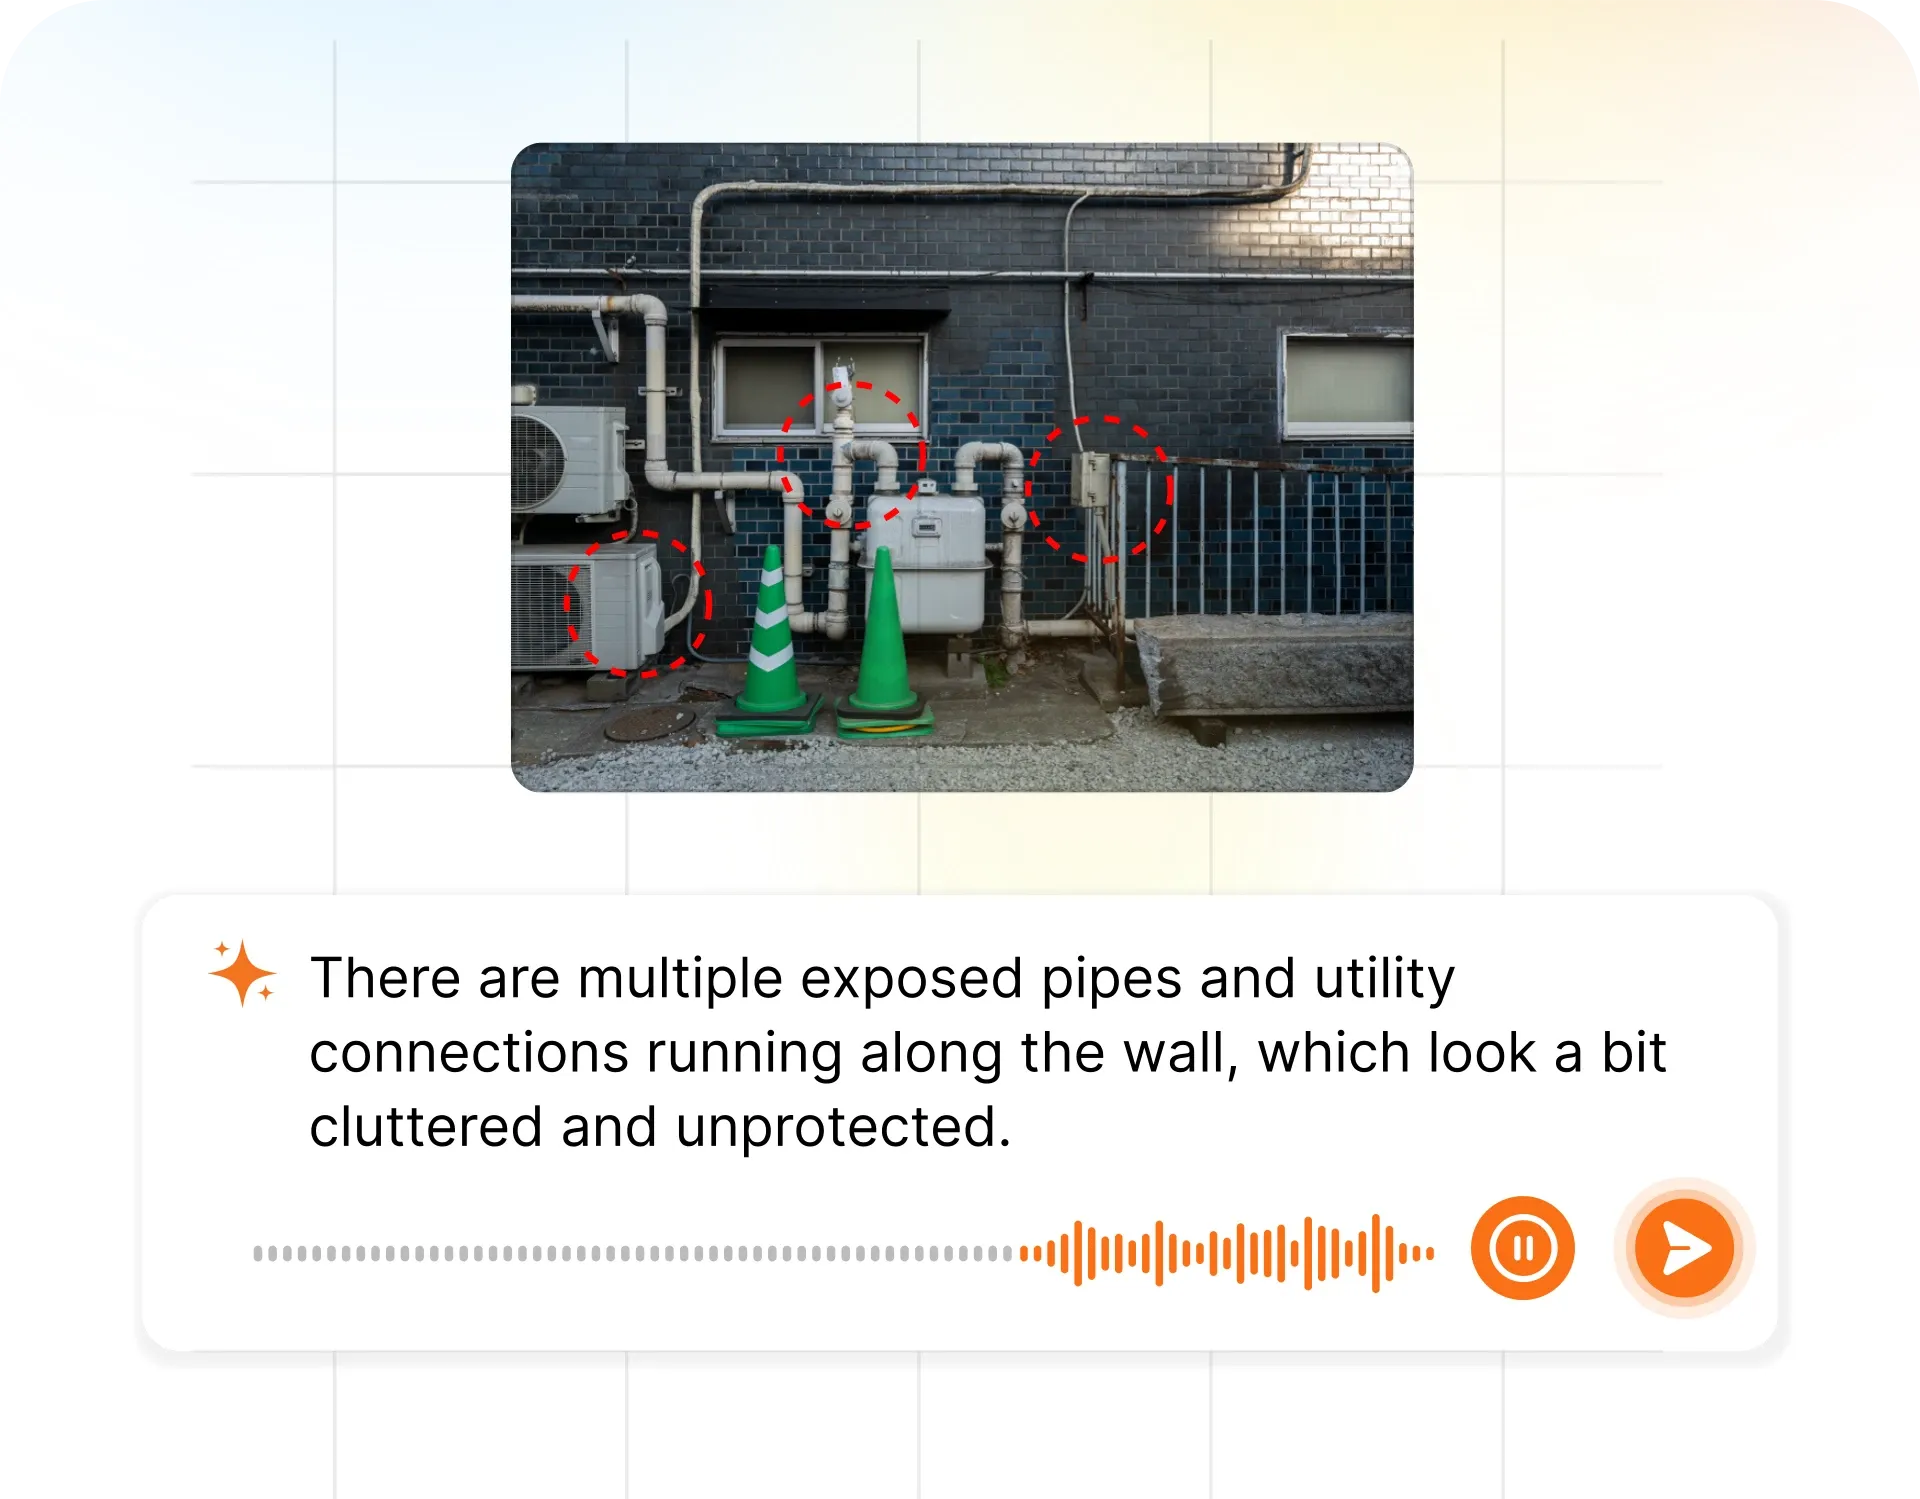
Inspectors speak their observations in any language. AI transcribes and fills the form in real time. Completely hands-free in the field.
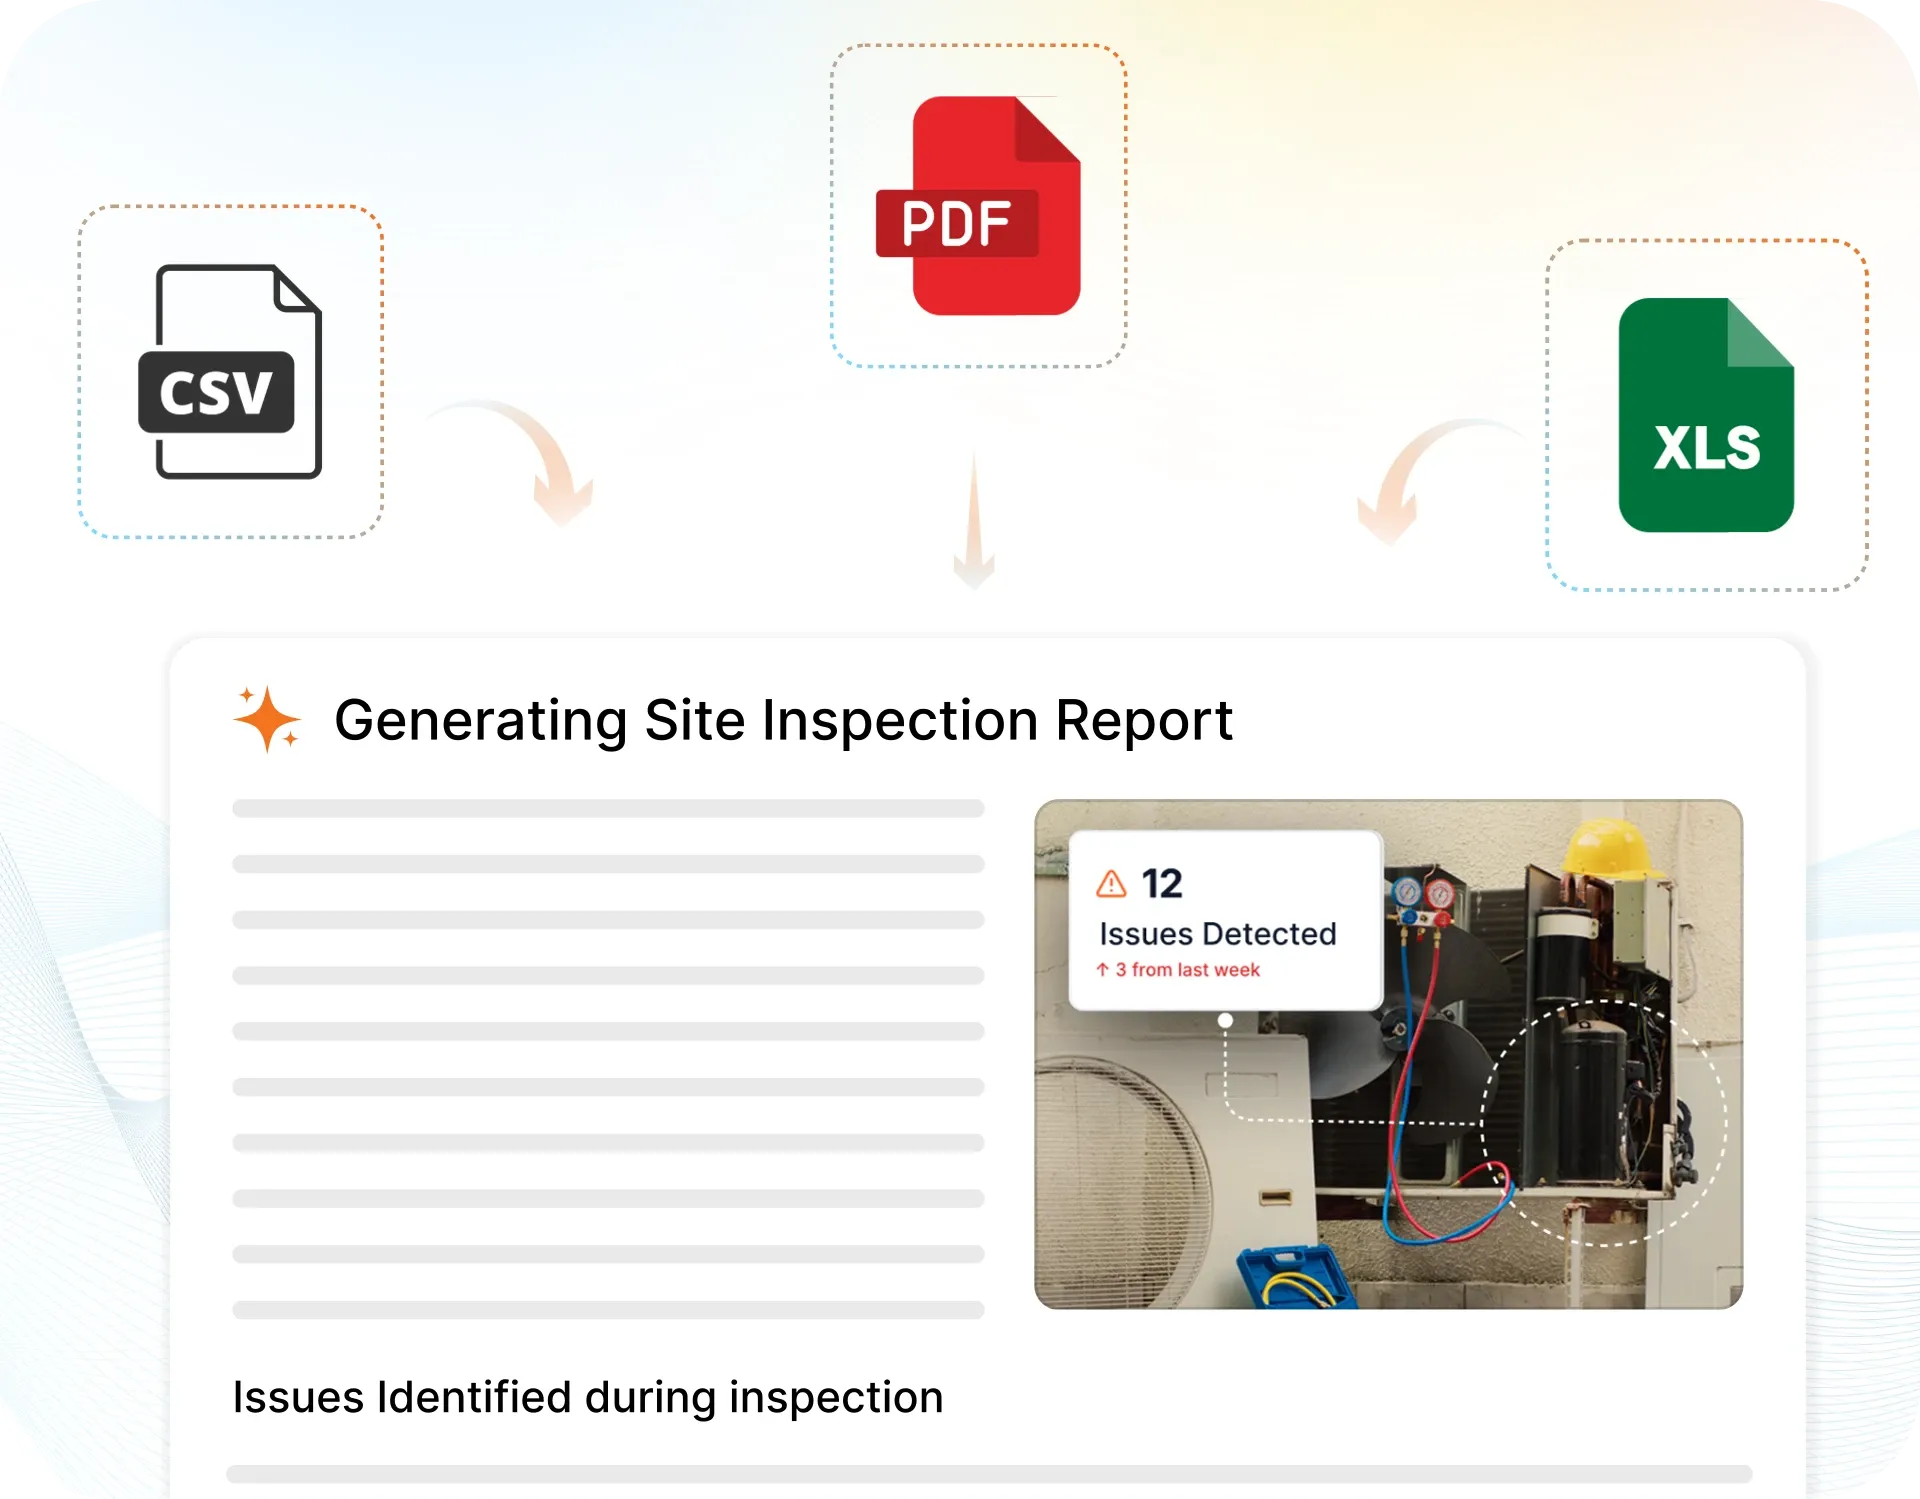
The moment an inspection is submitted, a branded PDF, Excel, or CSV report generates automatically. No manual work. No waiting.
InspectWrk integrates with the tools your team already uses, including Zoho, Microsoft 365, and SAP. No double entry.
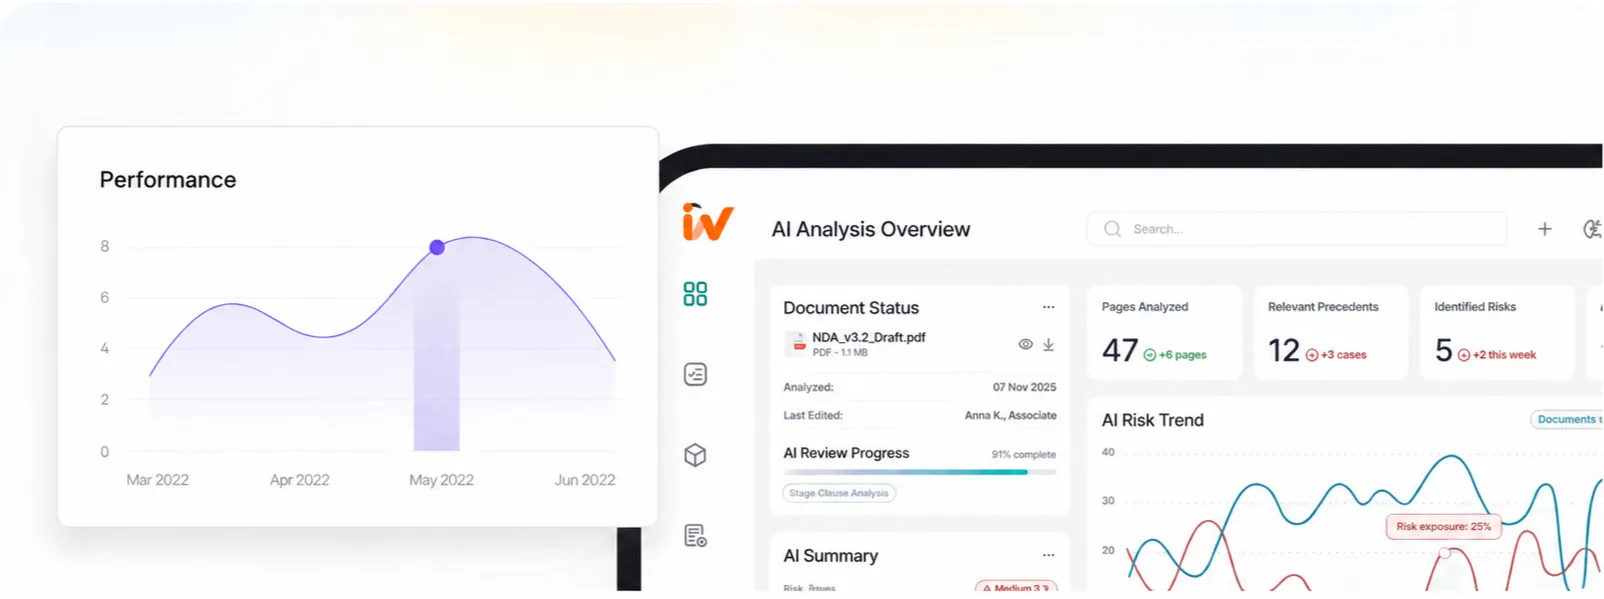
Your operations team sees completion rates, open issues, and compliance scores across all sites in real time. No chasing updates.
From data collection to compliance: see how teams use InspectWrk for every use case.
Capture field data once with digital forms that work even offline.
Explore use caseRun standardized inspections with photos, scoring, and instant reports.
Explore use caseConduct structured audits with evidence trails and pass or fail scoring.
Explore use caseLog hazards, near misses, and safety checks from any job site.
Explore use caseCatch defects early with repeatable quality checks and sign off.
Explore use caseReport incidents in the moment with photos and follow up actions.
Explore use caseInspect assets and keep condition and inspection history per asset.
Explore use caseRun preventive maintenance checks and log repairs with photo evidence.
Explore use caseStay audit ready with logged checks, timestamps, and shareable reports.
Explore use caseISPS Security work breaks down the moment evidence leaves the form. These are the problems ISPS Security Audit App is built to remove, and what the team gets back when it does.

There is no live view of ISPS security status across sites. The first sign that something failed on the asset is a client call or an incident, by which point the problem is already public.
Problem
Solution

One auditor is strict, another is lenient, and a third skips sections. The ISPS security audit scores come back, but leadership cannot tell whether a low score means a weak site or a tough auditor.
Problem
Solution

A failed item is noted during a routine audit. Nobody owns it, no date is set, and the next audit finds the same problem on the same asset. The ISPS security issue is logged, not closed.
Problem
Solution
ISPS Security Audit App runs a scored ISPS security audit against ISPS Code and SOLAS Chapter XI-2, checking security level and declaration of security, access control and restricted areas, CCTV, lighting, and perimeter, security equipment and communications, and drills, records, and training. Each finding is logged with a photo, a severity, and the point it fails, then routed to an owner with a deadline. It stays open until a reviewer verifies the fix, so the audit becomes a traceable evidence pack for ship and port facility security officers rather than an ageing spreadsheet. Because scoring is built into the template, two sites assessed by two people produce numbers you can compare fairly.
The audit targets the ISPS security failures that matter most: access control gaps at the security level, restricted areas unsecured, CCTV or lighting coverage gaps, and drills or records not maintained. Left unchecked, a fault such as access control gaps at the security level can mean downtime, a safety incident, or a failed audit, so every finding becomes an owned task with a deadline. It stays open until photo proof of the repair is reviewed, and repeat problems are flagged so ship and port facility security officers fix the cause rather than the symptom. Prioritising by severity means the most serious issues are handled first, not whichever was reported loudest.
ISPS Security Audit App keeps ISPS security checks aligned to ISPS Code and SOLAS Chapter XI-2. The photos and readings each standard expects are required fields, so an incomplete check cannot be closed and a gap is caught before an assessor finds it. When a review is due, ship and port facility security officers pull the records for the site in scope with one search instead of rebuilding them from folders. Retention and history stay searchable, so proof remains defensible at any point, not only on the day of an audit.
Yes. ISPS Security Audit App is offline-first: teams complete ISPS security checks on iOS or Android with no signal, capturing photos and the evidence each check requires in the field. Each record syncs automatically when the connection returns, with its timestamp intact, and the same template runs on every site. So ship and port facility security officers get a live view of what is complete, overdue, or failing per location, and a weak connection in a remote or low-signal area never costs a round or loses a photo.
Every completed ISPS security audit carries access control photo, restricted area photo, and drill record, a GPS location, a timestamp, and a named sign-off. Because the evidence is captured during the round rather than typed up afterwards, ship and port facility security officers can show exactly what was checked, when, and by whom. When an assessor or client asks, the record exports in seconds as a branded PDF or a searchable history, so proof never depends on someone remembering where a photo was saved or which folder holds last quarter's records.
Explore other inspection and audit apps for transport, logistics & warehousing teams.
Last updated: