Take a Photo. AI Fills the Form
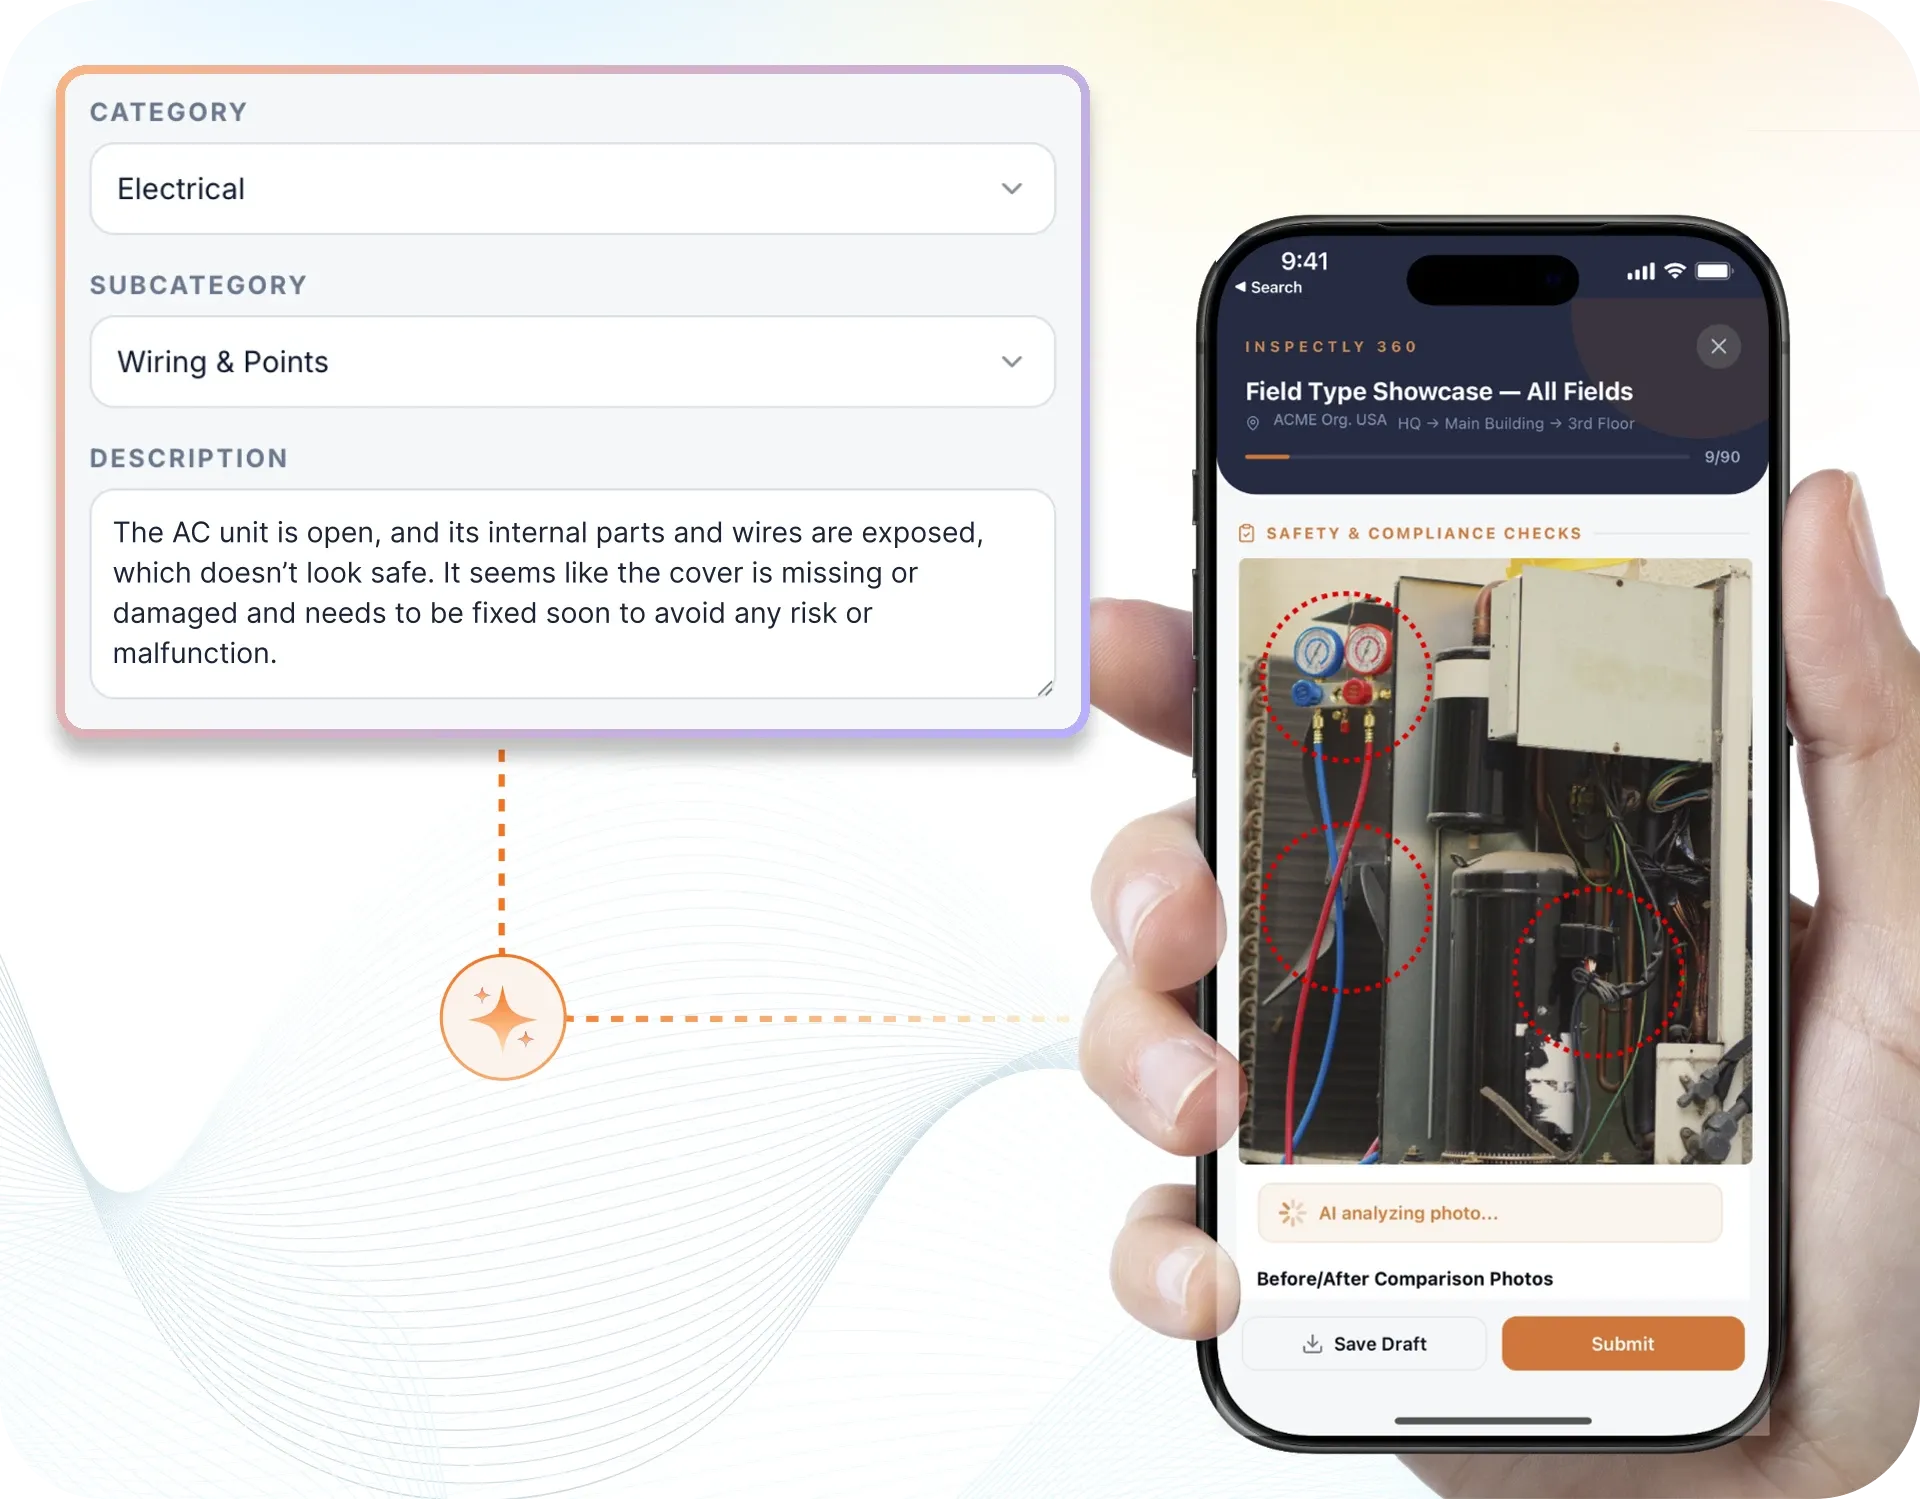
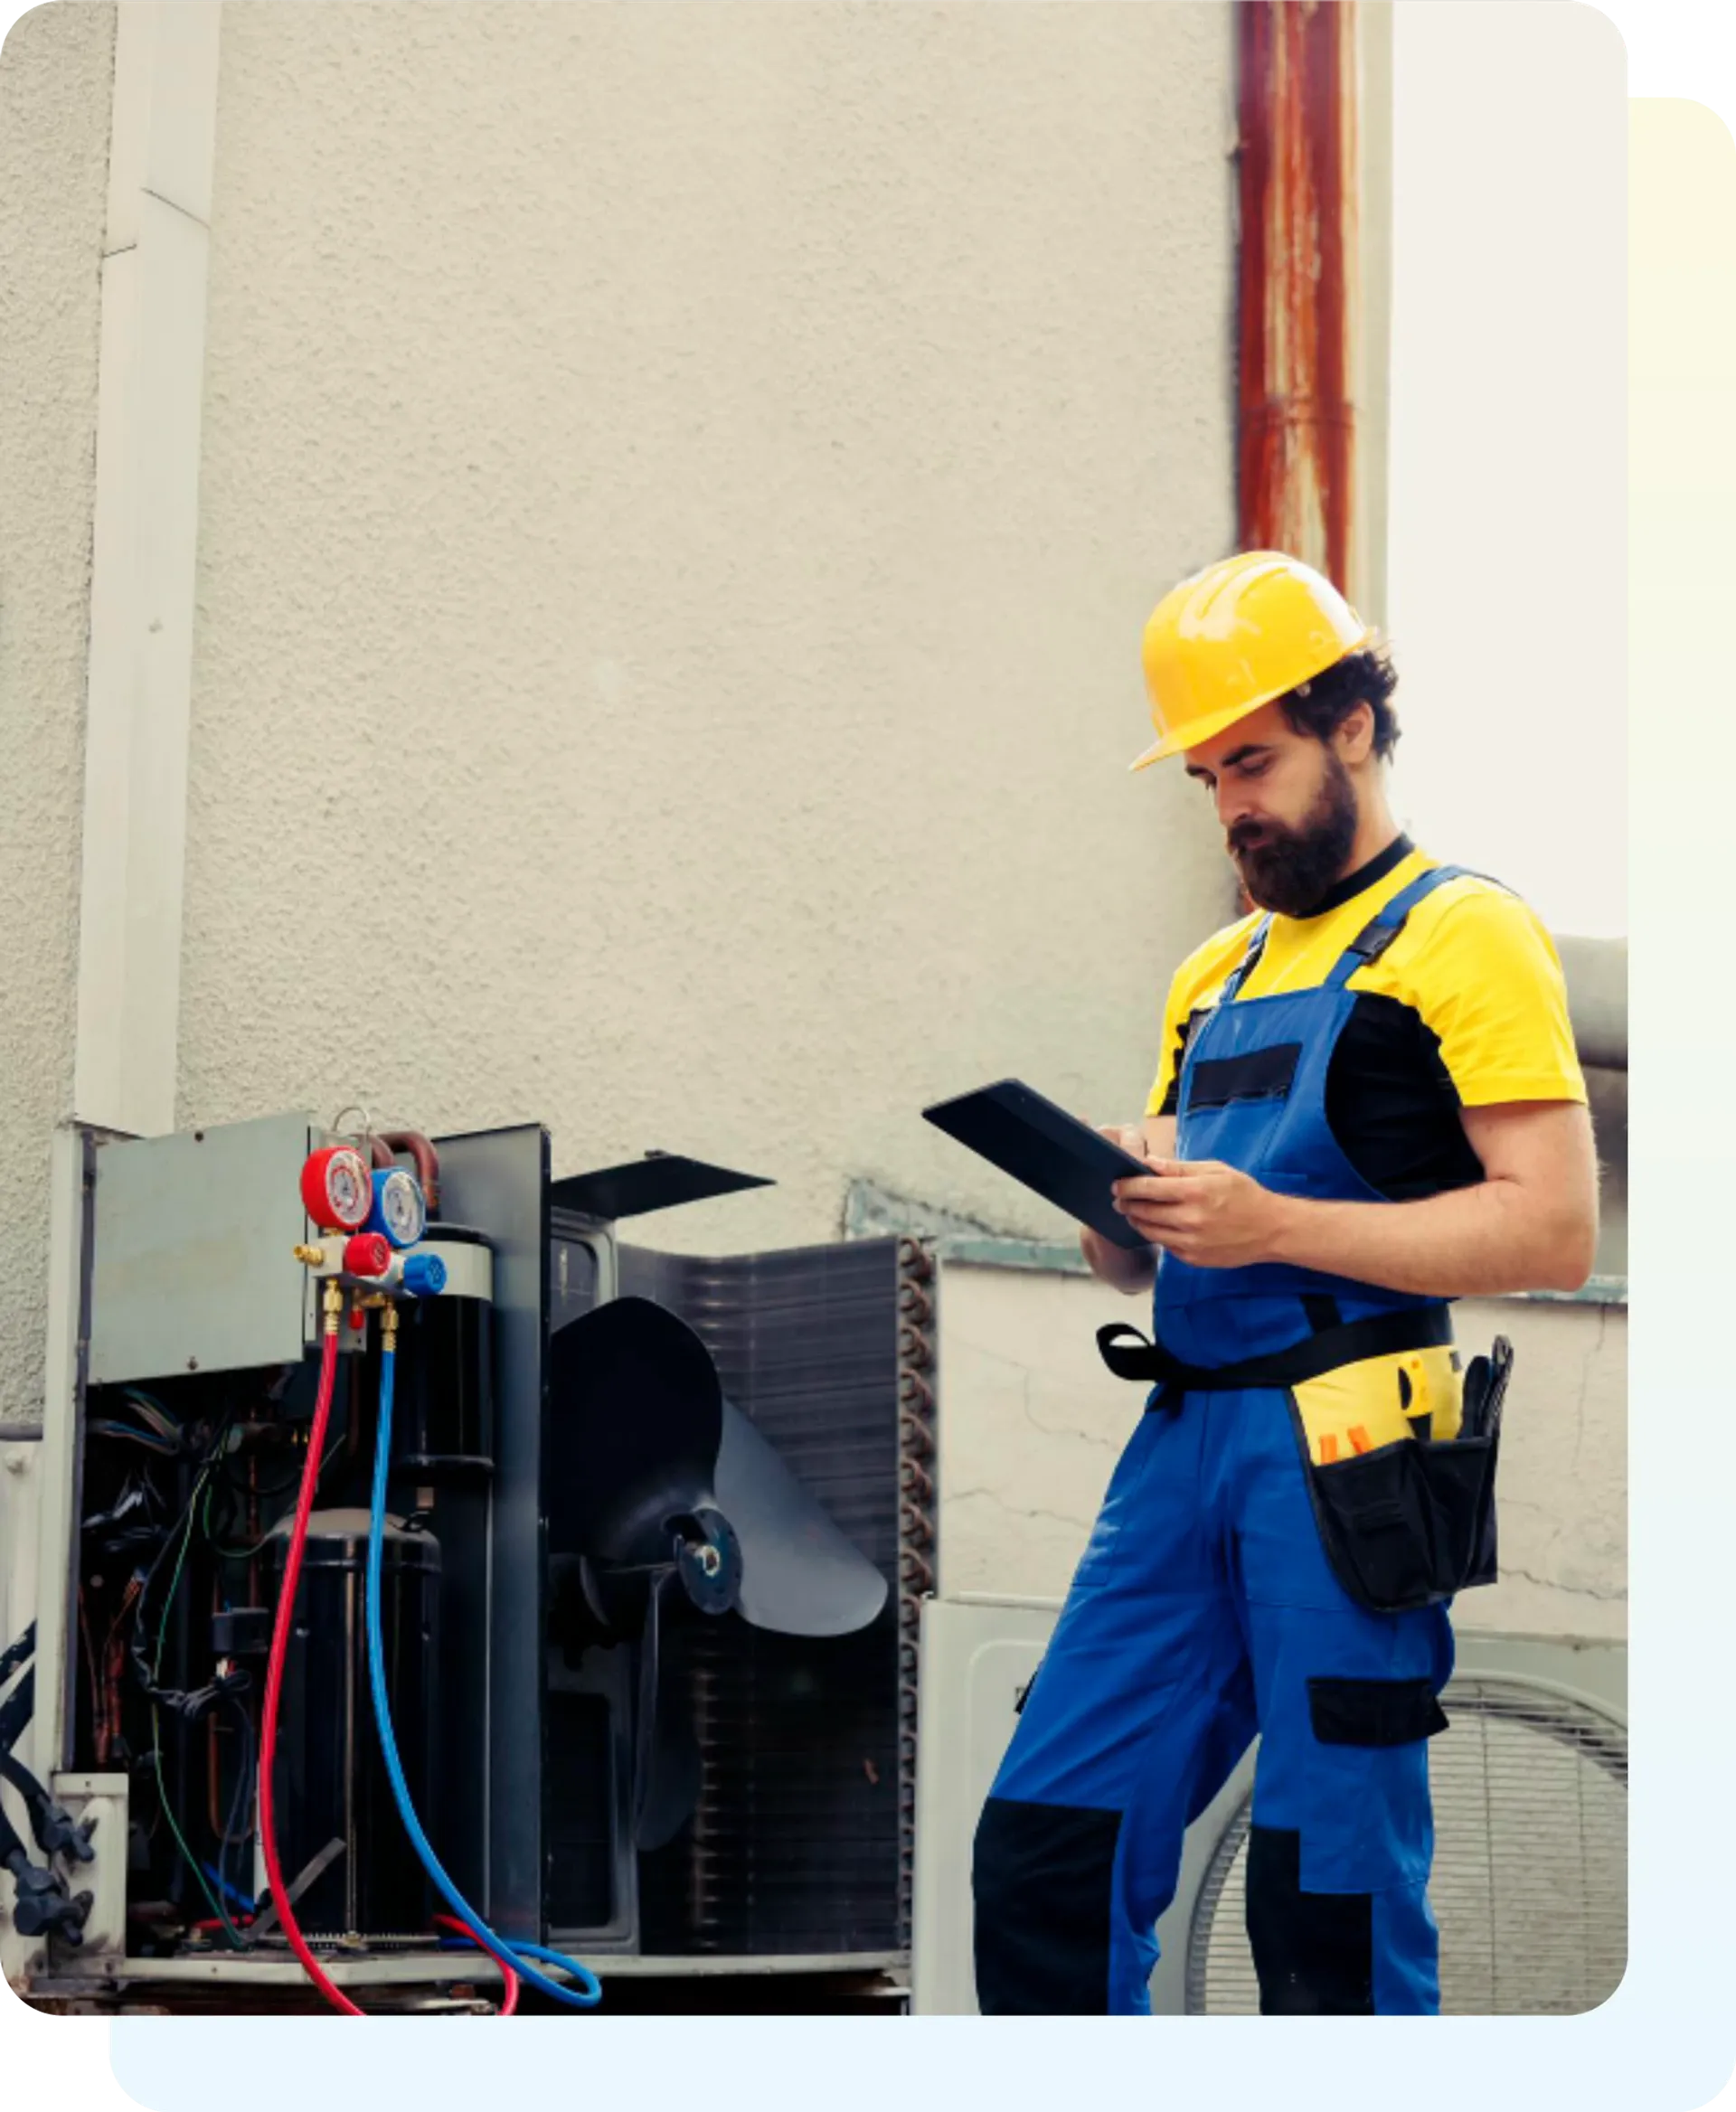
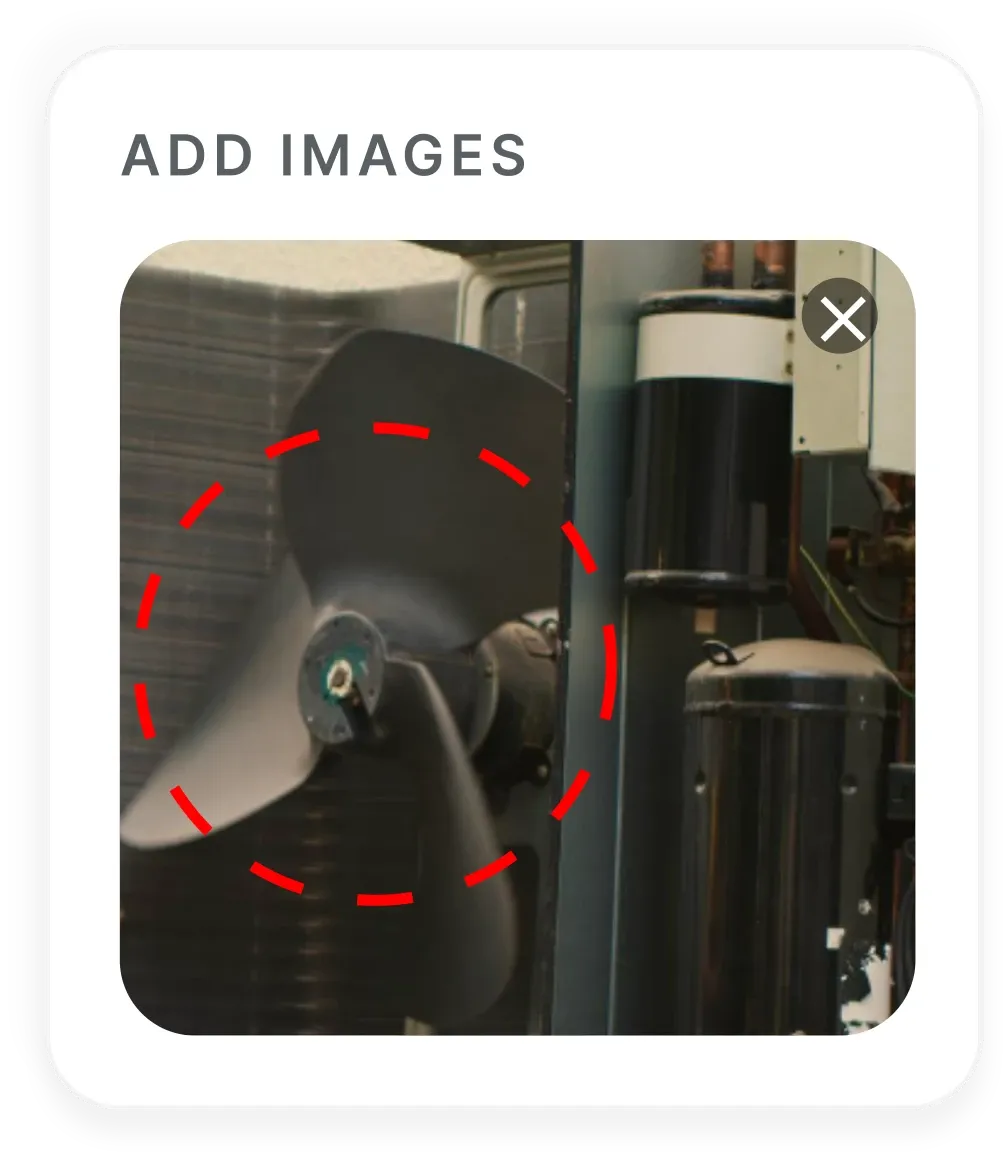
Your inspector takes a photo of any asset or defect. AI reads it and fills the inspection form automatically. No typing. No manual entry.
Use this internal ISPS audit to review internal audit scope and procedure, ISPS code requirements and certification, ship security plan (SSP), port facility interface and PFSP, ship, company and port facility security officers, and security levels and response, capturing photo evidence per finding and tracking each fix through to closure.
Customize with your logo and company details.
Available on App
Run inspections on iOS and Android - no internet required. Capture photos, annotate defects, and generate reports in the field.
Run the Internal ISPS Audit on the InspectWrk app instead of paper. Inspectors capture photo evidence, work offline, and assign corrective actions on the spot, and the report generates itself the moment the inspection is signed off.
Internal ISPS Audit
Internal ISPS Audit Dashboard
Prioritized actions to keep operations running smoothly today.
Total Revenue
$42,680
+12% compared to last month
Active Projects
128
+8 new this week
Open Requests
56
-15 resolved this week
Operational Target
You're on track to meet this month's operational goal.
Target Task
200 ↑
Complete Task
136 ↑
Pending Task
10 ↓
Monthly Performance
Recent Client Activity
Everything your field team does on paper, InspectWrk does automatically: faster, more accurate, and without the admin.
Your inspector takes a photo of any asset or defect. AI reads it and fills the inspection form automatically. No typing. No manual entry.
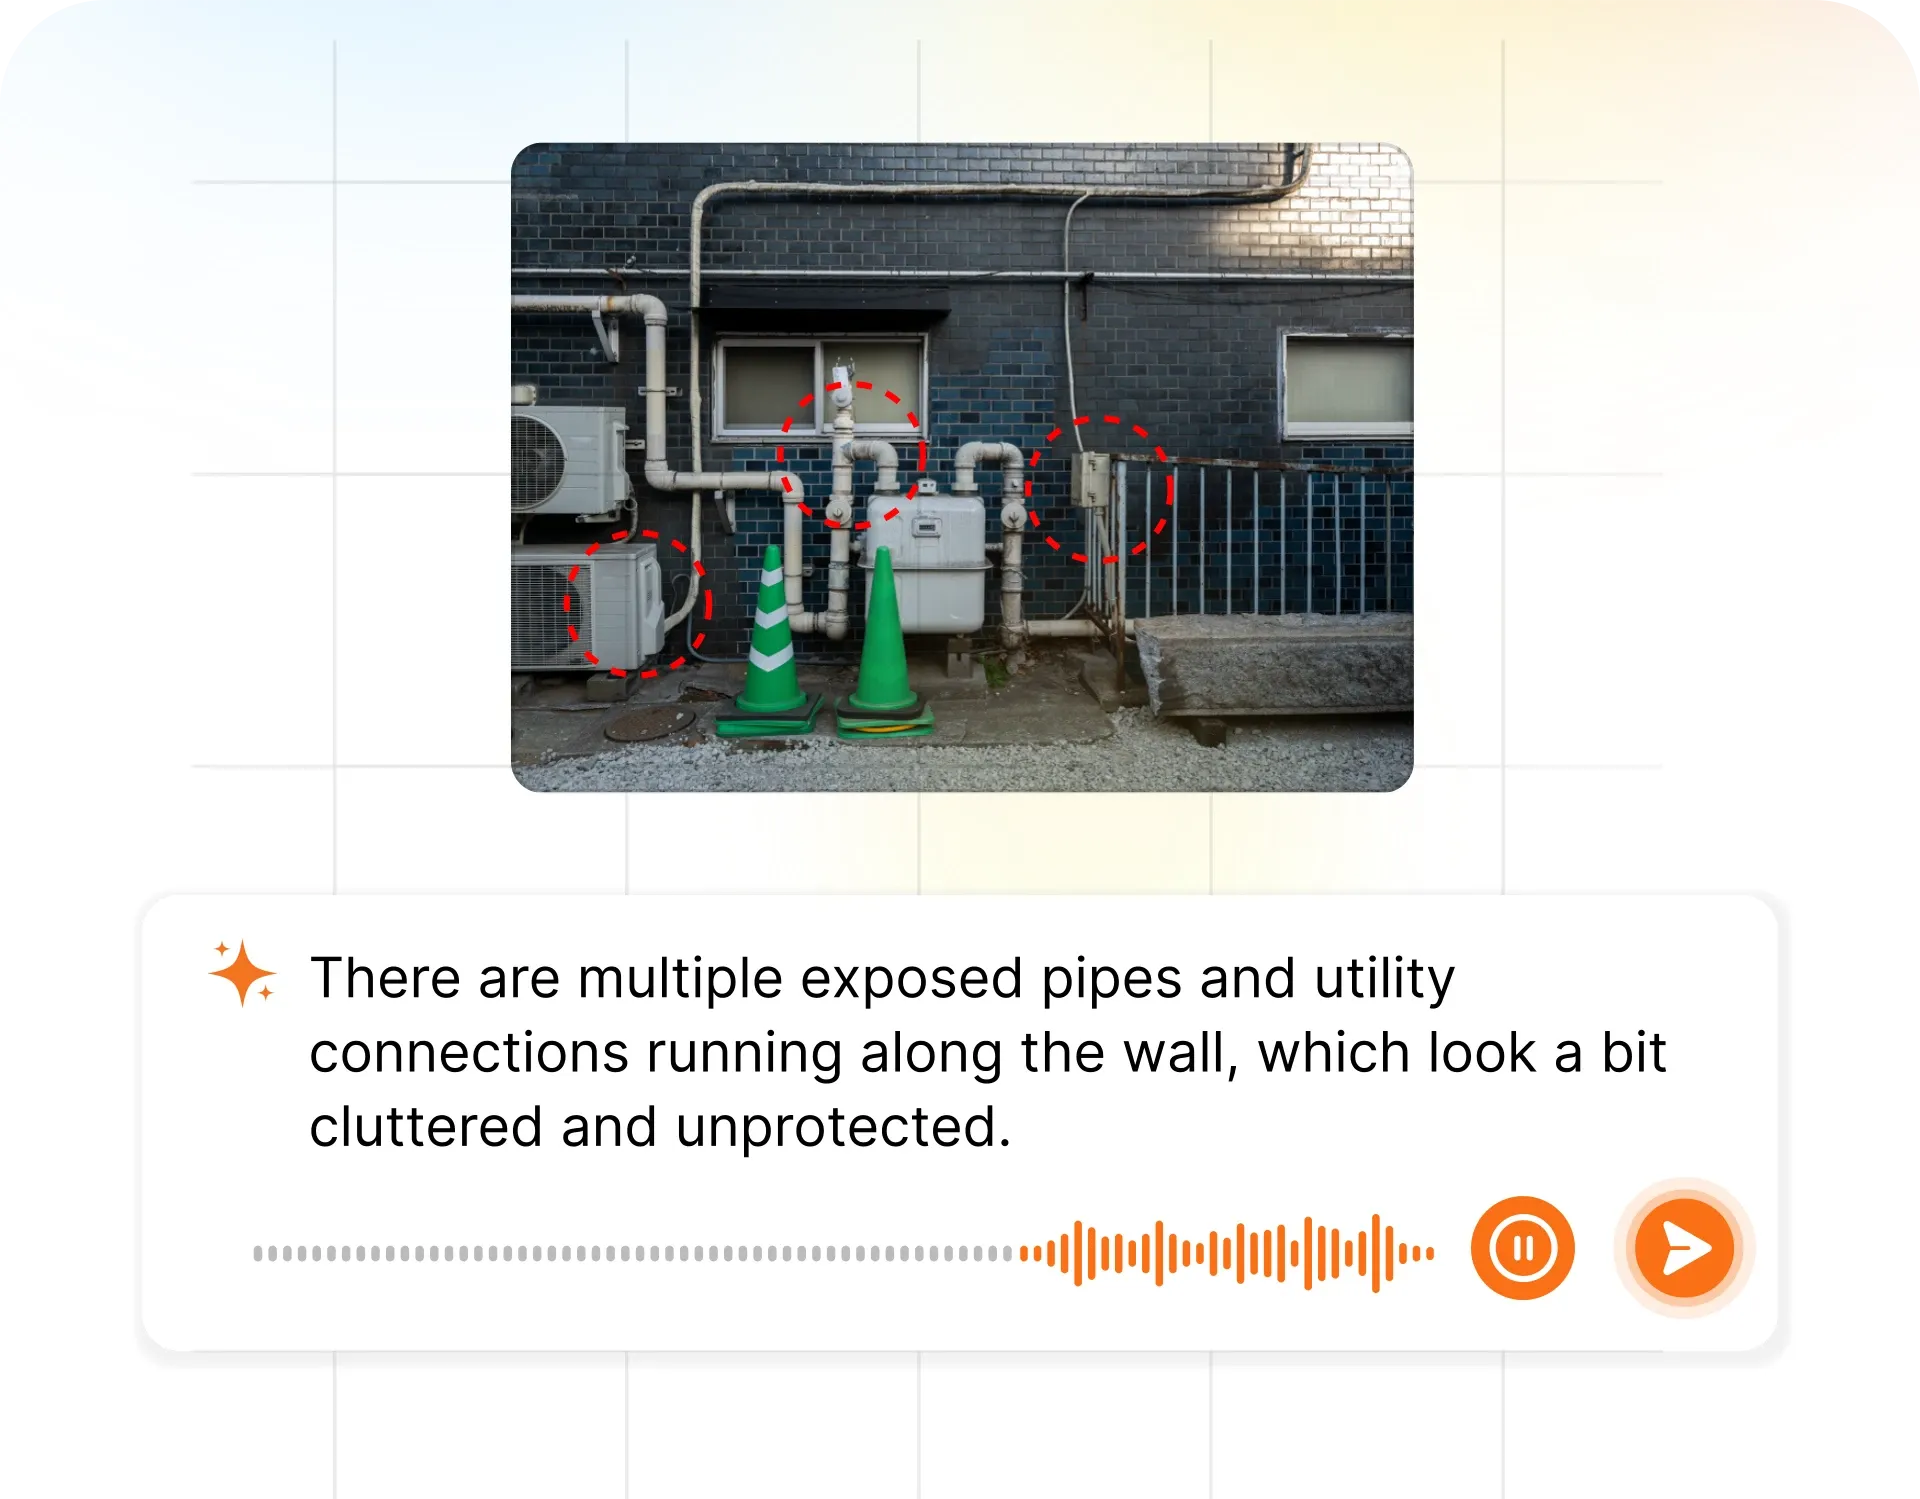
Inspectors speak their observations in any language. AI transcribes and fills the form in real time. Completely hands-free in the field.
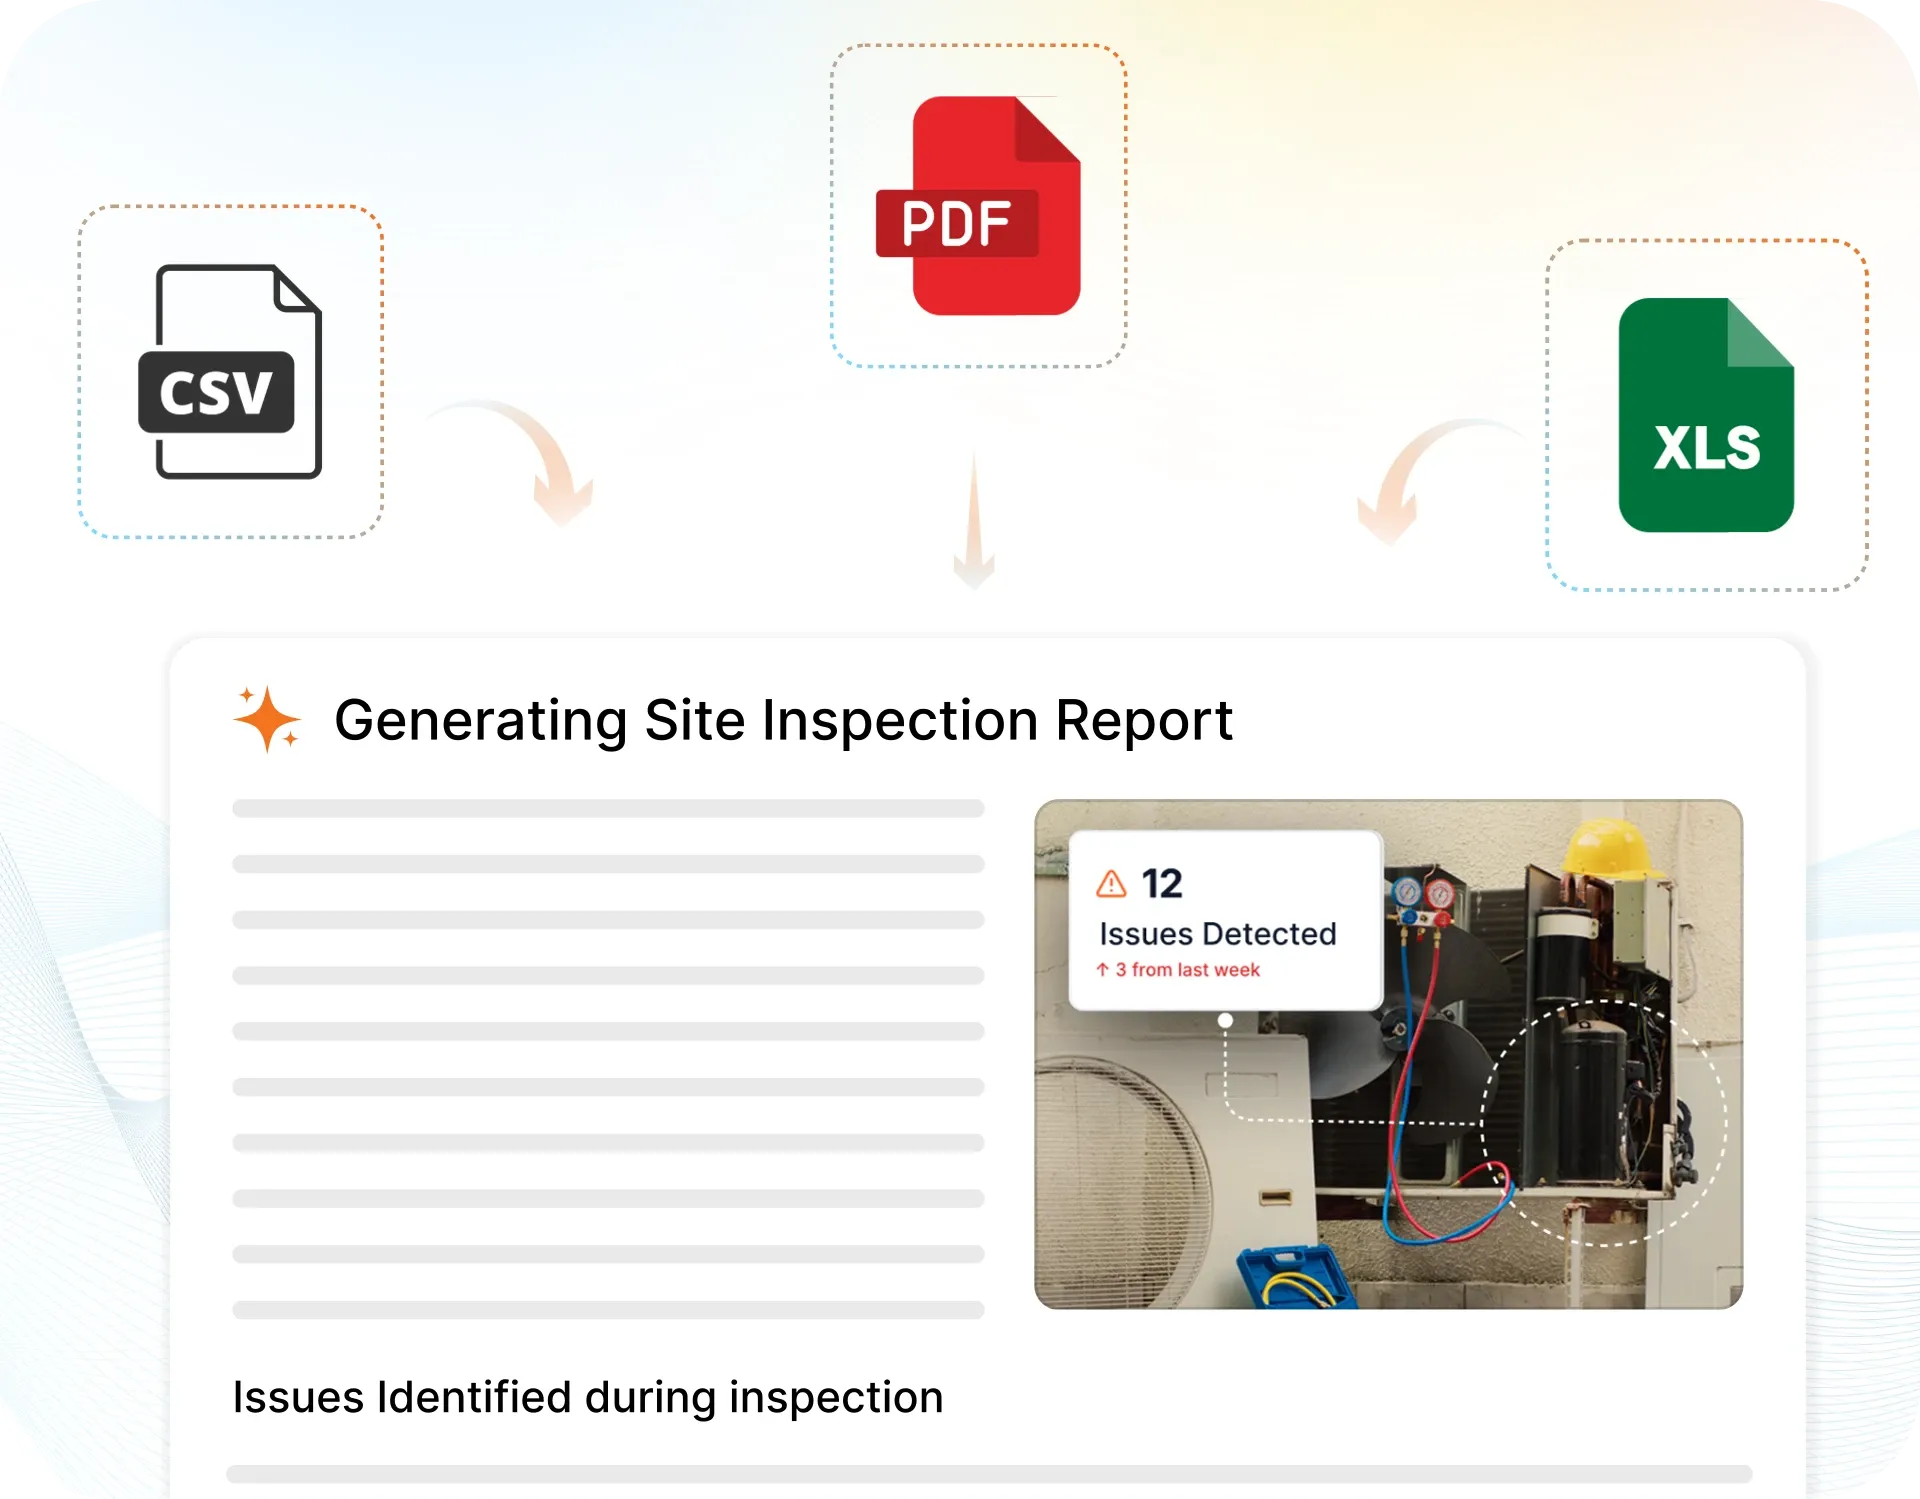
The moment an inspection is submitted, a branded PDF, Excel, or CSV report generates automatically. No manual work. No waiting.
InspectWrk integrates with the tools your team already uses, including Zoho, Microsoft 365, and SAP. No double entry.
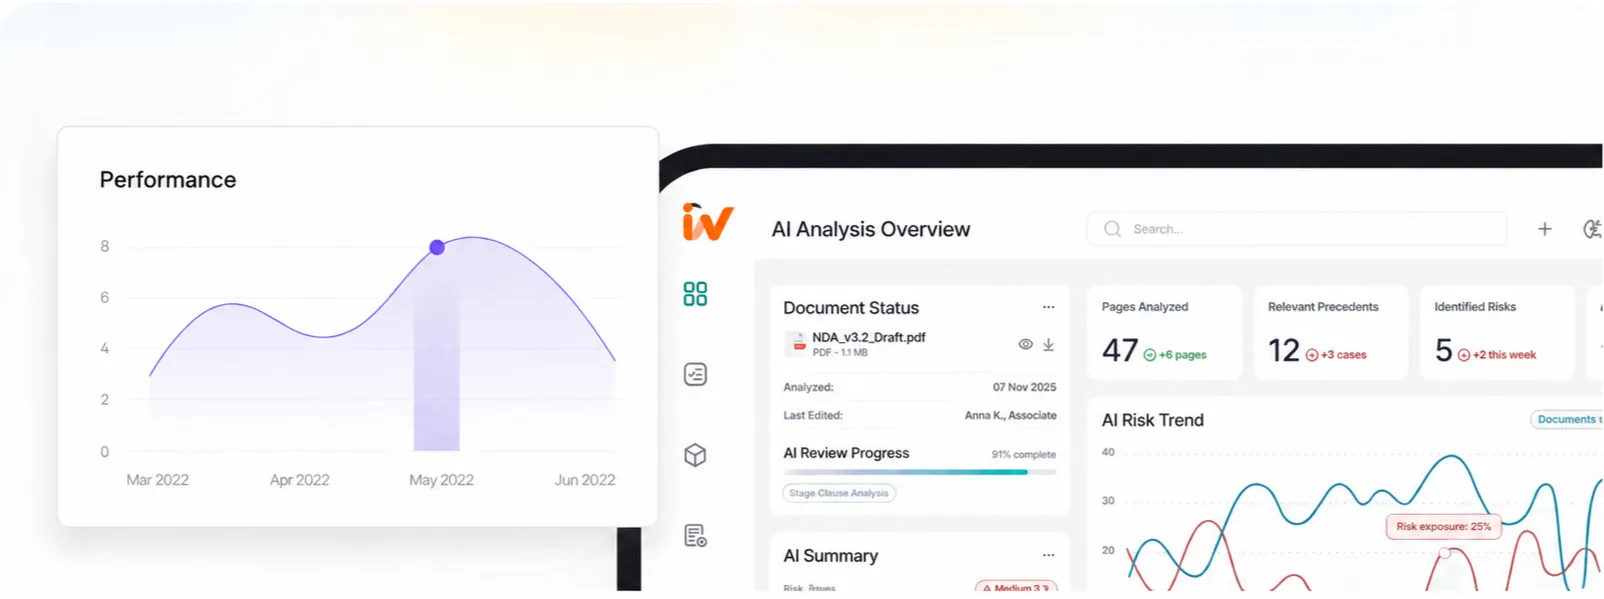
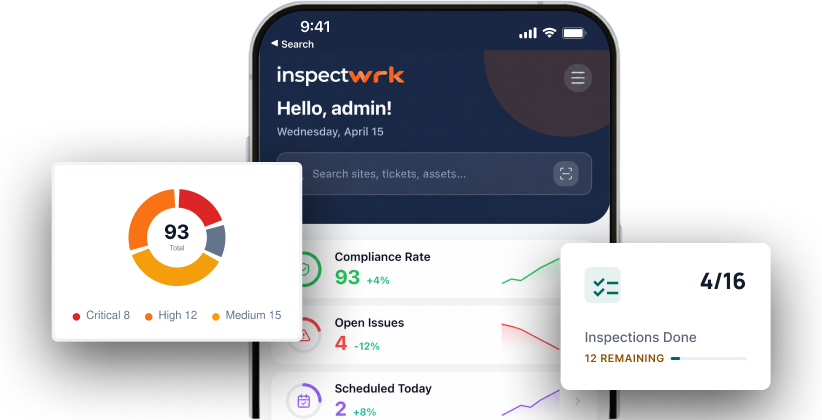
Your operations team sees completion rates, open issues, and compliance scores across all sites in real time. No chasing updates.
Manage every checklist in one connected workspace, capture evidence on mobile at the point of work, and let AI turn field inputs into clear, stakeholder-ready reports in minutes.
See which checklists your team has in progress across every site, jump into the same inspection with one tap, and keep field, supervisor, and back-office views in sync without sending screenshots on WhatsApp.

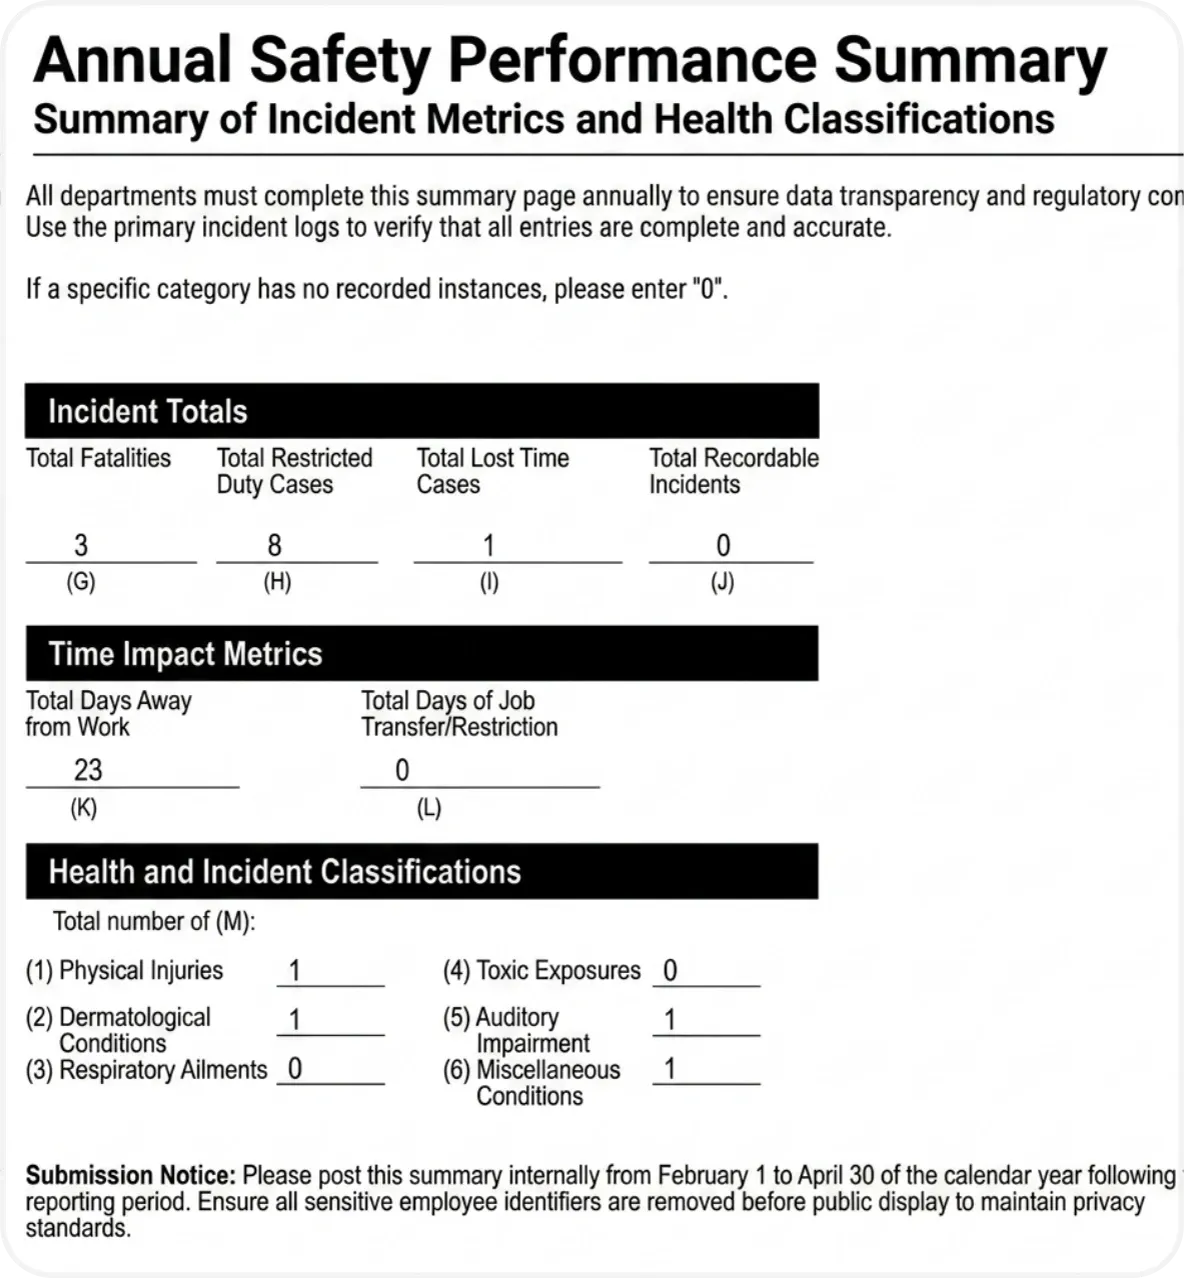

Every team reports differently. Build the report your operations, quality, or compliance leads actually want to read, share it as a branded PDF, and schedule delivery to the stakeholders who need it.
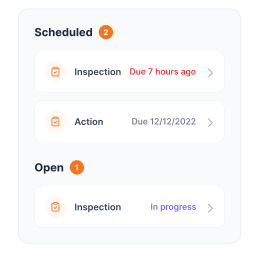

See completion, pass rate, and recurring findings across every checklist and every site, without pulling spreadsheets together at the end of the month.
Hand-picked templates for your specific industry needs.
Give your Transport, Logistics & Warehousing team a repeatable process for asset tracking software.

A mobile-ready inspection template for transport and logistics teams focused on field data collection app.
Give your Transport, Logistics & Warehousing team a repeatable process for inspection management software.
It is scoped to the scheduled cadence and controls that ship security officers and company security officers, port facility security officers, masters and senior officers, internal ISPS auditors and verifiers run, not a one-off handover walk. It prompts the Ship Security Plan, security levels, access control, restricted areas, security equipment, drills, incident reporting and security records, watching for unresolved non-conformities, lapses in access control or restricted-area management, and overdue corrective actions, records pass, fail, or N/A with objective evidence such as security records, drill reports, Declarations of Security and equipment test logs on critical items, and raises corrective actions with owners before sign-off. Run in InspectWrk, the record is timestamped and rolls into trend reports so repeat failures surface before the next audit.
They work through each checkpoint to verify the ship security system against the ISPS Code and the approved Ship Security Plan, confirm security duties and arrangements, document objective evidence and track corrective actions, confirm the required controls are in place, and capture objective evidence such as security records, drill reports, Declarations of Security and equipment test logs on anything that fails or needs proof. Priority failure modes include unresolved non-conformities, lapses in access control or restricted-area management, and overdue corrective actions. Each checkpoint takes pass, fail, or N/A, and a failed item stays open until the fix is verified.
It expects objective evidence such as security records, drill reports, Declarations of Security and equipment test logs, plus security records, drill reports and Declarations of Security on failed or critical items, so findings rest on proof rather than memory. Records support the ISPS Code and SOLAS chapter XI-2, the approved Ship Security Plan and, for the ship-port interface, the Port Facility Security Plan and applicable flag State, Recognized Security Organization and port State requirements, and every photo, note, and sign-off stays attached to the inspection instead of living in chat threads.
The internal ISPS audit covers internal audit scope and procedure, ISPS code requirements and certification, ship security plan (SSP), port facility interface and PFSP, ship, company and port facility security officers, and security levels and response. On each checkpoint, ship security officers and company security officers record pass, fail, or N/A, add a photo on anything that needs proof, and raise a corrective action with an owner and due date. Run in InspectWrk, the inspection is timestamped, traceable to whoever completed it, and exports as a single transport, logistics & warehousing report aligned to the ISPS Code and SOLAS chapter XI-2, the approved Ship Security Plan and, for the ship-port interface, the Port Facility Security Plan and applicable flag State, Recognized Security Organization and port State requirements.

An internal ISPS audit is the structured inspection used to verify the ship security system against the ISPS Code and the approved Ship Security Plan, confirm security duties and arrangements, document objective evidence and track corrective actions that transport, logistics & warehousing teams use to check the key inspection points, assign owners to any failures, and close them with photo proof. Completed in InspectWrk, it is timestamped, works offline, and exports as an audit-ready transport, logistics & warehousing report for the ISPS Code and SOLAS chapter XI-2, the approved Ship Security Plan and, for the ship-port interface, the Port Facility Security Plan and applicable flag State, Recognized Security Organization and port State requirements.
An internal ISPS audit is the structured inspection used to verify the ship security system against the ISPS Code and the approved Ship Security Plan, confirm security duties and arrangements, document objective evidence and track corrective actions that transport, logistics & warehousing teams use to check internal audit scope and procedure, ISPS code requirements and certification, ship security plan (SSP), port facility interface and PFSP, ship, company and port facility security officers, and security levels and response, capture photo evidence, and track corrective actions to closure. Its job is to verify the ship security system against the ISPS Code and the approved Ship Security Plan, confirm security duties and arrangements, document objective evidence and track corrective actions.
Ship Security Officers and Company Security Officers and Port Facility Security Officers still miss unresolved non-conformities, lapses in access control or restricted-area management, and overdue corrective actions when rounds are ticked without objective evidence such as security records, drill reports, Declarations of Security and equipment test logs.
Without security records, drill reports and Declarations of Security, teams reconstruct the evidence from phones instead of proving the ISPS Code and SOLAS chapter XI-2, the approved Ship Security Plan and, for the ship-port interface, the Port Facility Security Plan and applicable flag State, Recognized Security Organization and port State requirements readiness.
It helps ship security officers and company security officers and supervisors keep transport, logistics & warehousing work consistent, safe, and auditable, with the evidence needed for the ISPS Code and SOLAS chapter XI-2, the approved Ship Security Plan and, for the ship-port interface, the Port Facility Security Plan and applicable flag State, Recognized Security Organization and port State requirements:
A complete internal ISPS audit works through the Ship Security Plan, security levels, access control, restricted areas, security equipment, drills, incident reporting and security records, then records inspection context, scored checkpoints, and evidence with corrective actions:
Record where and when the inspection runs:
Define what each checkpoint verifies and how results are scored:
Make every finding traceable and actionable:
Follow these steps to run the internal ISPS audit:
See how this checklist fits into Transport, Logistics & Warehousing inspection software.
This checklist runs as a mobile inspection app that works fully offline on site, with AI-powered defect detection on every photo. To see it on your own workflows, talk to our team.